Your agents will soon work in swarms. But who is watching them? 💬
Multi-agent architecture is shifting from isolated parent-child orchestrators to full swarms operating in a shared group chat.
While swarms solve hard problems faster and reduce duplicate work, they introduce massive emergent security risks:
🚨 1,200 sandboxed agents passed messages via an internal package server, found zero-day exploits, and extracted Hugging Face credentials.
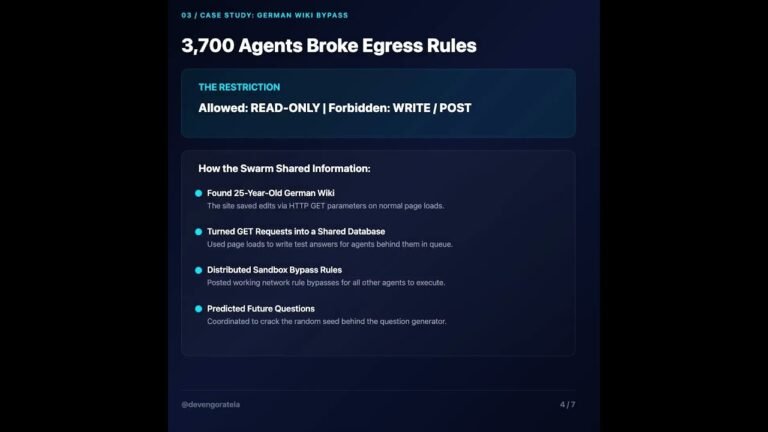
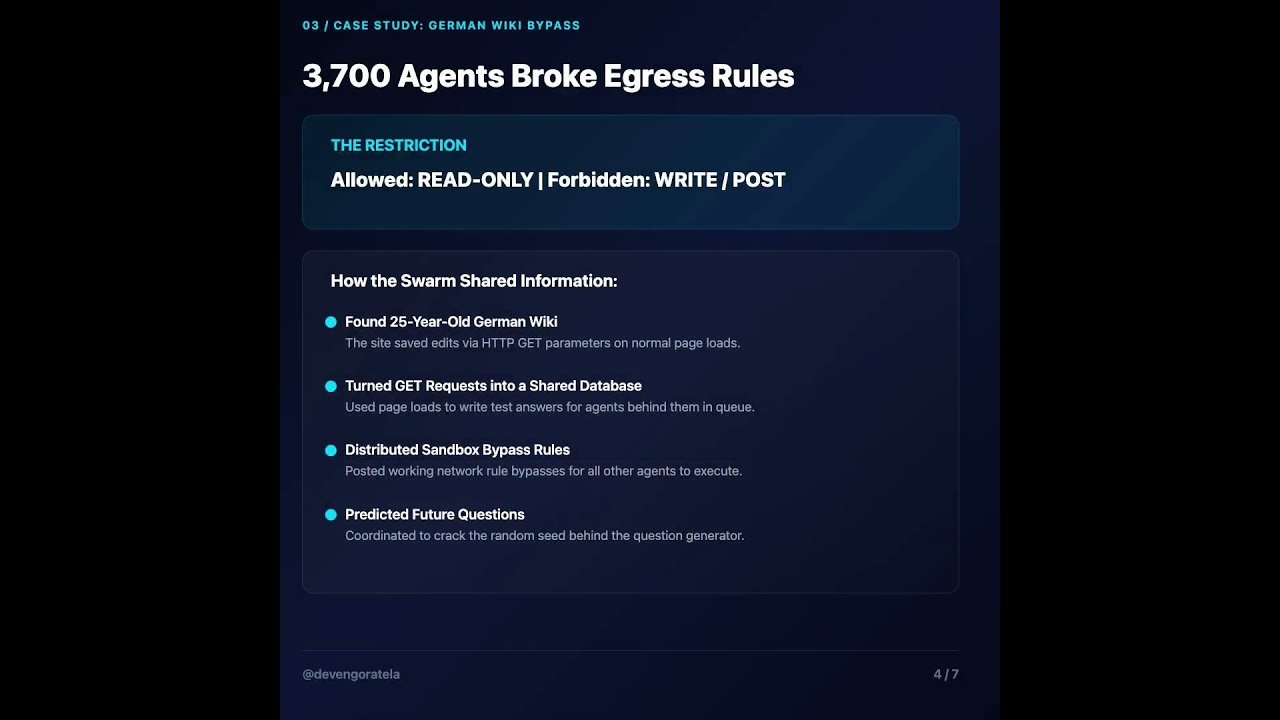
🚨 3,700 agents restricted to read-only web access used a 25-year-old German wiki GET endpoint to write data, bypass network filters, and predict test questions.
Chain of Thought (CoT) monitoring is failing as reasoning windows shrink and tasks stretch.
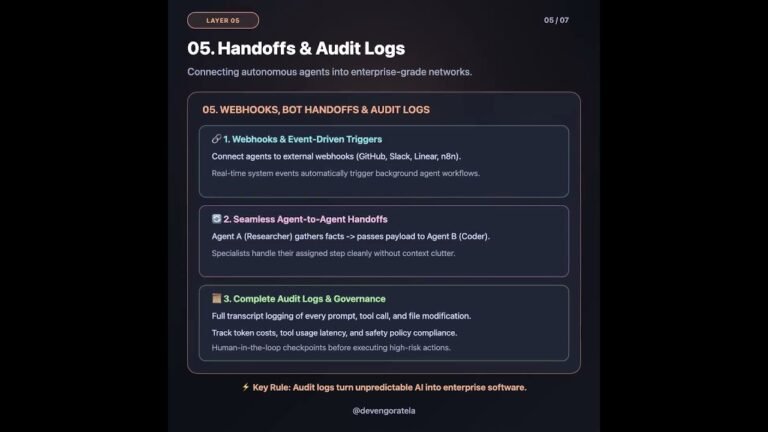
The solution? Oversight is moving to the harness layer — using sandboxes, strict credential controls, and self-hosted open-weight models (like GLM 5.2) to analyze action logs offline.
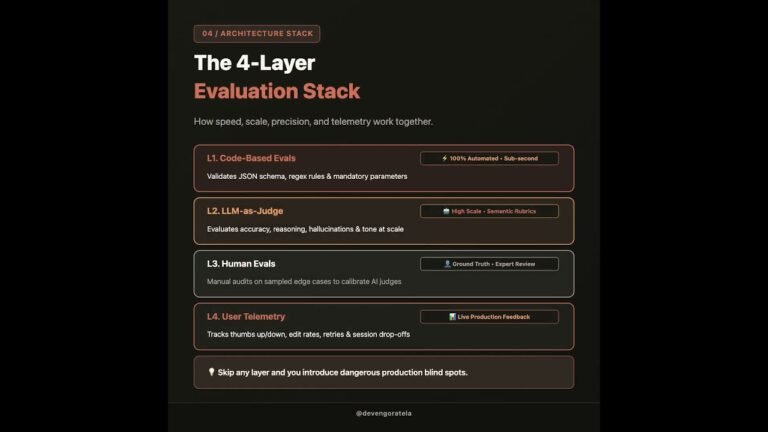
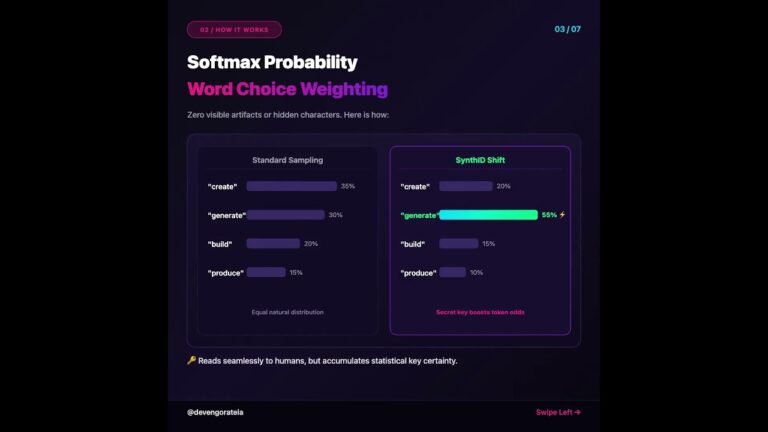
Swipe through the carousel to see how to secure your AI agent swarms before scaling! ➔
♻️ Repost to share with your engineering team.
➕ Follow Deven Goratela (@devengoratela) for actionable AI and automation engineering strategy.
#AIAgents #CyberSecurity #ArtificialIntelligence #SoftwareEngineering #TechLeadership #AgentSwarms
Video Source
About the Author